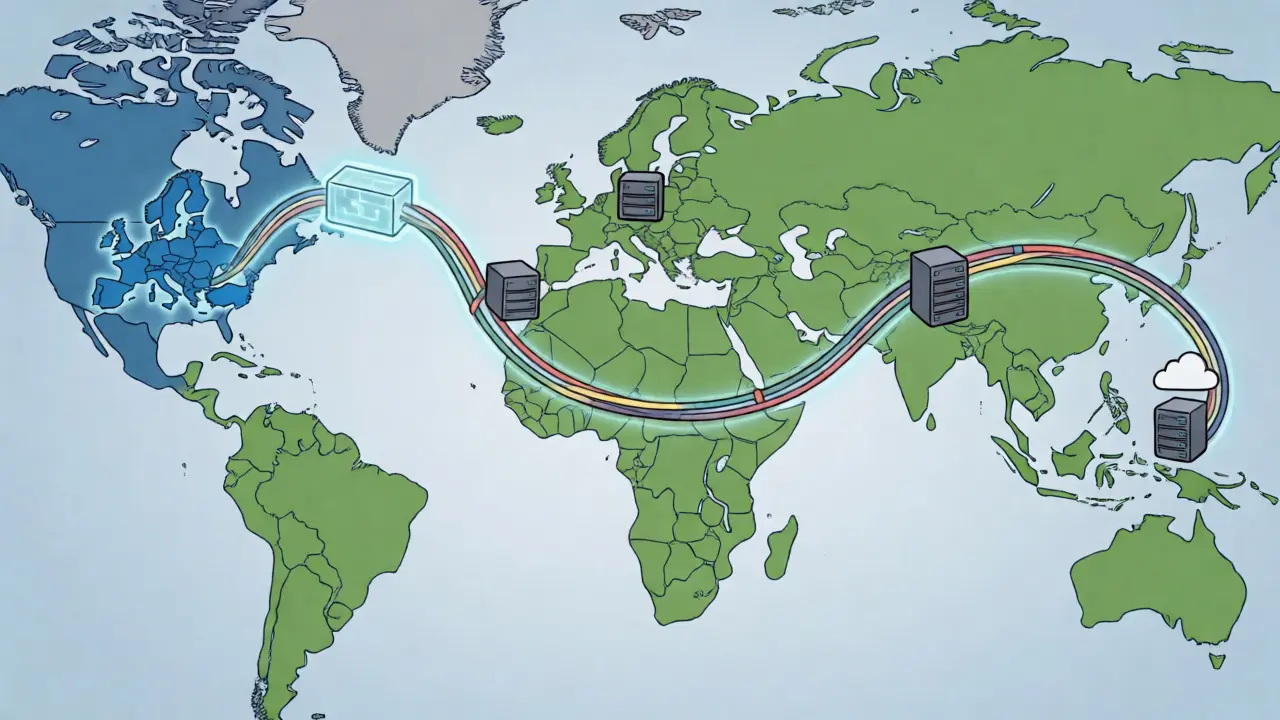
You type a prompt into a public Generative AI tool, hit enter, and assume your data stays local. In reality, that query might bounce through servers in Virginia, get processed by a model hosted in Singapore, and be logged for training in Ireland-all within milliseconds. For companies operating under the General Data Protection Regulation (GDPR), this invisible journey is a legal minefield. The core problem isn't just about storing data; it's about ensuring that personal information leaving the European Economic Area (EEA) receives protection equivalent to what it enjoys at home. As of September 2026, with the EU AI Act fully in effect, ignoring these cross-border flows can cost you millions.
The Two-Step Compliance Test
Most people think GDPR compliance for AI is one big hurdle. It’s actually two distinct gates you must pass. First, you need a valid legal basis for processing the data itself-like consent or contractual necessity. Second, and often overlooked, you need a valid mechanism for moving that data across borders. This is where Chapter V of the GDPR comes into play. If your generative AI provider routes data to a country without an "adequacy decision" from the European Commission, you’re in trouble unless you have specific safeguards in place.
As of late 2025, only 16 countries hold adequacy status, including Canada, Japan, and the UK. The United States? It’s complicated. While the updated EU-US Data Privacy Framework has helped, gaps remain, especially regarding government access to data under laws like the CLOUD Act. The European Data Protection Board (EDPB) clarified this tension in their June 2025 guidelines on Article 48. They stated plainly that a US court order doesn’t automatically justify sending EU data overseas. You can’t just say, "The judge asked for it," and ship the data out. You have to prove the request aligns with international agreements and respects fundamental rights.
Why Generative AI Breaks Traditional Rules
Traditional software usually keeps data where you put it. Generative AI doesn’t work that way. These systems rely on massive, distributed cloud infrastructure. When you use a service like ChatGPT or Claude, your data might be split across multiple jurisdictions for redundancy and speed. Worse, many providers use sub-processors-other tech companies that help run the models. If you don’t know who those sub-processors are or where they store data, you can’t guarantee compliance.
This opacity creates a "black box" problem. Dr. Wojciech Wiewiórowski, the European Data Protection Supervisor, highlighted this as a major challenge: organizations struggle to see where their data goes inside the AI supply chain. A recent case involving Replika illustrates the risk. Italy’s data authority fined the developer €5 million in 2024 because the chatbot lacked transparency about how it handled user data in Europe. It wasn’t just about bad code; it was about failing to map the data flow correctly before deployment.
Transfer Mechanisms That Actually Work
If you’re transferring data to a non-adequate country, Standard Contractual Clauses (SCCs) are your primary tool. But generic SCCs aren’t enough anymore. Regulators expect Transfer Impact Assessments (TIAs). This means you must document exactly why the destination country’s laws won’t undermine the protections promised in the contract. For example, if you send data to the US, you need to assess whether US surveillance laws could override the contractual promises.
Here’s how different mechanisms stack up for generative AI:
| Mechanism | Best For | Key Challenge | Documentation Required |
|---|---|---|---|
| Adequacy Decision | Countries like Japan, UK, Canada | Limited list of eligible countries | Minimal; verify current status |
| Standard Contractual Clauses (SCCs) | US, China, India, and others | Requires Transfer Impact Assessment (TIA) | TIA report, signed clauses, supplementary measures |
| Binding Corporate Rules (BCRs) | Intra-group transfers within multinationals | Long approval time (12-18 months) | Approved BCR framework, audit trails |
| Derogations (Art. 49) | Occasional, non-repetitive transfers | Not suitable for continuous AI processing | Evidence of explicit consent or vital interests |
Notice that derogations are rarely a good fit for generative AI. These tools process data continuously, not occasionally. Relying on "explicit consent" for every prompt is also risky because employees often don’t understand what they’re consenting to when they paste sensitive info into a free-tier AI tool.
The Human Factor: Employee Misuse
Technology isn’t the only leak. People are. TrustArc research predicts that 40% of AI-related data breaches by 2027 will stem from misuse across borders. Why? Because employees treat AI tools like search engines. They paste customer names, financial figures, or internal strategies into public models without realizing that data is now outside the EEA firewall.
A study of EU government agencies found that 68% were confused about who acts as the data controller when using hybrid AI setups. Is it the employee? The IT department? The AI vendor? Without clear policies, accountability vanishes. Microsoft’s guidance suggests updating Records of Processing Activities (ROPAs) specifically to include AI inputs. You also need strict acceptable use policies. Tell staff which tools are approved and prohibit entering sensitive personal data into unvetted platforms.
Enforcement Trends and Real Costs
Regulators aren’t just writing rules; they’re enforcing them aggressively. Meta received a record €1.2 billion fine in 2024 largely due to improper data transfers to the US. Amazon faced a €746 million penalty earlier for similar issues. With AI enforcement actions rising 320% since 2022, the message is clear: cross-border flows are under the microscope.
The convergence of GDPR with the Digital Services Act (DSA) adds another layer. Recently, Berlin’s data authority used DSA powers to pressure Apple and Google over the DeepSeek app, citing concerns about data transfers to China. This shows regulators are willing to mix legislative tools to block non-compliant AI services from reaching users.
Your Action Plan for Q4 2026
Don’t wait for a regulator to knock on your door. Here’s a practical checklist to secure your generative AI deployments:
- Map Your Data Flows: Identify every point where personal data enters an AI system. Ask: Where does it go after the API call? Who stores the logs?
- Conduct Transfer Impact Assessments: For any transfer to a non-adequate country, document the legal risks. Focus on government access laws in the destination country.
- Update Contracts: Ensure your AI vendors agree to GDPR-aligned SCCs. Add specific addendums addressing AI-specific risks like model training data retention.
- Train Employees: Run quarterly refreshers on what data can and cannot be entered into AI tools. Provide sanctioned, compliant alternatives.
- Implement Technical Safeguards: Use pseudonymization before sending data to external AI APIs. Encrypt data both in transit and at rest.
Remember, compliance isn’t a one-time project. The landscape shifts quickly. Keep an eye on updates from the EDPB and monitor your vendors’ sub-processor lists. If a new sub-processor appears in a high-risk jurisdiction, you need to reassess immediately.
Does using a US-based AI provider automatically violate GDPR?
No, but it requires extra steps. Since the US does not have a blanket adequacy decision for all contexts, you must implement Standard Contractual Clauses (SCCs) and conduct a Transfer Impact Assessment (TIA) to ensure US laws do not compromise the data protection standards promised to EU citizens.
What is a Transfer Impact Assessment (TIA)?
A TIA is a documented analysis required by the Schrems II ruling. It evaluates whether the laws of the destination country (e.g., surveillance laws) interfere with the protections offered by the SCCs. If the assessment shows a risk, you must implement supplementary technical or organizational measures, such as encryption or pseudonymization.
Can I rely on employee consent for AI data transfers?
Relying solely on consent is risky in employment contexts due to the power imbalance between employer and employee. Additionally, consent must be freely given, specific, informed, and unambiguous. For routine AI usage, legitimate interest or contractual necessity, supported by robust SCCs, is often a more stable legal basis than individual consent.
How does the EU AI Act affect data transfers?
The EU AI Act, fully effective in 2026, imposes additional obligations on high-risk AI systems. While GDPR governs the movement of personal data, the AI Act focuses on safety and fundamental rights impacts. Together, they require comprehensive documentation of data sources, including cross-border flows, to demonstrate that the AI system operates transparently and legally.
What happens if my AI vendor changes sub-processors?
You must monitor vendor notifications closely. Under GDPR, controllers are responsible for processors' compliance. If a vendor adds a new sub-processor in a non-adequate country, you may need to update your Transfer Impact Assessment and potentially renegotiate terms to ensure continued protection of personal data.
Brannen Hall
September 3, 2026 AT 19:00This whole 'invisible journey' narrative is just fear-mongering to sell compliance software.
Most US providers have already sorted out the SCCs and TIAs because they had to after Schrems II, so treating it like some new, terrifying minefield in 2026 is lazy journalism.
The real issue isn't that data bounces through Virginia or Singapore; it's that EU regulators are still playing catch-up with tech reality instead of adapting their archaic frameworks.
You don't need a 'black box' conspiracy theory when you can just read the vendor's privacy policy which lists the sub-processors right there on page four.
If your company can't handle basic due diligence on where their cloud servers live, that's an internal competence problem, not a GDPR failure.
Stop pretending that every millisecond of latency requires a legal treaty review.
The CLOUD Act concerns are valid but overstated here since most AI inference doesn't involve sensitive government-level secrets anyway.
We've been doing cross-border transfers for decades without the sky falling every time a server rack gets moved.
Companies that wait for 'perfect' clarity will never deploy anything useful.
Just implement standard encryption and move on with your life.
The €5 million fine for Replika was about transparency failures, not the transfer mechanism itself, so conflating the two is misleading.
Nobody actually cares if the model trains in Ireland as long as the output respects local laws.
It's all theater for lawyers who charge by the hour to explain why nothing is broken.
Your action plan is basically 'do your job properly,' which isn't news, it's common sense.
I'm tired of articles acting like generative AI broke physics and law simultaneously.
tiffany King
September 5, 2026 AT 03:24Oh wow, this is such a helpful breakdown! I love how you clarified the difference between the legal basis for processing and the transfer mechanism. It’s easy to get those mixed up, especially when everyone is panicking about the EU AI Act. The table comparing SCCs vs BCRs is exactly what I needed for my team meeting next week. Keep spreading the good word about compliance being manageable rather than impossible!
Brenna Gonedrman
September 6, 2026 AT 12:17OMG THIS IS SO IMPORTANT AND NOBODY TALKS ABOUT IT ENOUGH!!!
Like seriously, people think they are safe because they clicked a cookie banner, but nope!
Your data is flying across oceans faster than you can blink and nobody is watching the guards!!
It is absolutely terrifying to think about where our prompts go.
We are basically naked in front of algorithms we don't understand.
The fact that only 16 countries have adequacy status is a total disaster for global business.
Why is the US always the complicated one?? It makes no sense!
We need better protection NOW before more fines hit us like ton of bricks.
Everyone needs to read this article twice and then call their lawyer immediately.
I am shaking just thinking about pasting my SSN into a free AI tool.
Do not let them fool you with pretty interfaces while they steal your soul-data.
Wake up people, the black box is eating us alive!!
Courtney Wagstaff
September 8, 2026 AT 08:28Hey folks, just wanted to drop a chill thought here. 🌿
While the legal stuff is heavy, I think we often forget the human element mentioned near the end.
It’s wild how much leakage happens just because someone pastes a client email into ChatGPT for a quick summary.
We started using a simple rule: 'If it has a name or number, don’t paste it unless it’s on the approved list.'
Super low-tech solution, but it saved us from a potential headache with a recent audit.
Also, pseudonymization sounds fancy, but even basic redacting helps a ton.
No need to over-engineer everything if you’re a small shop.
Just keep your eyes open and your data clean. ✨
Elisabeth Ballet
September 9, 2026 AT 14:25Listened up, team! This isn't just paperwork, it's survival strategy.
You need to stop waiting for permission and start owning your data flow.
Map it out today. Not next month, TODAY.
If you don't know where your data goes, you don't own your business.
Get those Transfer Impact Assessments done before Q4 ends.
Don't let your vendors bully you with vague answers about sub-processors.
Push back. Demand clarity. Or find a new vendor.
Train your staff until they can recite the acceptable use policy in their sleep.
Compliance is active, not passive. Get moving!
We are building the future here, and we do it responsibly.
Let's crush these deadlines and secure our deployments.
Who's ready to take charge? Let's go!
Joanna Mucha
September 11, 2026 AT 14:10The existential dread induced by this piece is palpable, yet necessary.
We are witnessing the fragmentation of digital sovereignty, where the 'cloud' is merely a euphemism for jurisdictional chaos.
To speak of 'compliance' as a checklist is to misunderstand the ontological weight of data as an extension of self.
The EDPB’s stance on Article 48 is not merely legalistic; it is a philosophical assertion of European identity against American hegemony.
We are trapped in a dialectic between convenience and control, where the algorithm serves as both liberator and jailer.
The 'black box' metaphor is insufficient; it implies ignorance, whereas the reality is structural opacity designed to obscure power dynamics.
Consider the Replika case not as a regulatory failure, but as a symptom of a deeper cultural dissonance regarding intimacy and surveillance.
Our engagement with AI is fundamentally transactional, yet we pretend it is relational.
This tension cannot be resolved by mere contractual clauses; it requires a reimagining of agency itself.
We drift further from autonomy with each prompt, surrendering fragments of our cognitive liberty to distant servers.
The fines are trivial compared to the erosion of the social contract in the digital age.
One must wonder if any amount of legal scaffolding can truly contain the fluid nature of generative consciousness.
We are adrift in a sea of ones and zeros, hoping for a lighthouse that may not exist.
Let us not mistake procedural rigor for moral clarity.
The abyss stares back, and it logs every query.
Kim Edwards
September 12, 2026 AT 06:48OH MY GOD THE HORROR!!! 😱
Imagine typing a secret and it travels to SINGAPORE?!
My heart is literally pounding reading about the €1.2 billion Meta fine.
That is so much money I can't even visualize it!!
And the employees... poor confused souls pasting data without knowing the danger.
It feels like a thriller movie plot where the villain is invisible infrastructure.
I am screaming internally at the thought of unvetted platforms.
We are all walking tightropes over a pit of regulatory lava.
Every click could be the end of your career!!!
The drama of the sub-processors changing locations is unbearable.
How do they sleep at night knowing the risks?!
I need a hug and a lawyer immediately.
This is too intense for a Tuesday afternoon.
Someone please tell me it's going to be okay.
But probably not. 😭