You ask an AI to "write a quick login system." It spits out code in seconds. You deploy it. Two weeks later, you're explaining to your CTO why the database is public and your company just lost $85,000 cleaning up the mess. Sound familiar? This isn't bad luck; it's vibe coding gone wrong.
Vibe coding is the practice of asking Large Language Models (LLMs) for code based on general feelings or vague descriptions rather than precise technical specifications. While it feels productive, it often leads to insecure, inefficient, or buggy software. The problem isn't always the AI; it's how we talk to it. We call these problematic instructions anti-pattern prompts. These are specific types of questions that trick LLMs into generating vulnerable code because they lack critical context, security constraints, or version details.
If you want to stop firefighting bugs that never should have existed, you need to know what not to ask. Here is the reality: basic "write code" prompts without security considerations result in 64% higher weakness density in GPT-3 outputs and 59% higher in GPT-4 compared to structured prompts. Let’s look at exactly which prompts you should ban from your workflow and what to use instead.
The Cost of Being Vague
Why does being casual with your AI cost so much? Because LLMs are pattern-matchers, not security experts. They predict the next likely token based on training data. If most of their training data contains insecure implementations-which it does, since insecure code is prevalent in public repositories-the AI will likely give you insecure code.
A study analyzing the DevGPT dataset showed that context-free prompts required 3.7 times more iterations to get satisfactory results compared to structured ones. Think about that. You think you’re saving time by typing five words, but you’re actually spending hours debugging logic errors and security holes. GitHub’s 2024 State of the Octoverse report found that 68% of insecure AI-generated code submissions came from prompts that simply asked for functionality without any security constraints.
When you say, "Make this look nice," you are outsourcing your architectural decisions to a model that has no opinion on maintainability. When you say, "Handle user input," you are ignoring the fact that improper input validation is one of the top causes of vulnerabilities (CWE-20). The AI doesn't know if you mean a text field, a file upload, or a complex JSON payload unless you tell it.
Anti-Prompt #1: The "Just Make It Work" Request
This is the most common offender. You type: "Write a Python function to process user data."
It sounds harmless. But what kind of data? Where does it come from? What happens if it’s null? What format is it in? Without these answers, the AI guesses. And usually, it guesses the simplest path, which often skips error handling and validation.
| Prompt Type | Average Interactions Needed | Security Vulnerability Rate | First-Response Accuracy |
|---|---|---|---|
| Vague "Vibe" Prompt | 4.3 | High (64% increase) | Low |
| Structured Recipe Prompt | 1.2 | Low (72% reduction) | High (4.1x better) |
The fix? Be boringly specific. Instead of "process user data," try: "Generate a Python 3.11 function that validates a JSON payload containing 'email' and 'age'. Use Pydantic for validation. Return a boolean for validity and a list of error strings. Avoid CWE-20 (Improper Input Validation)."
See the difference? You specified the language version, the library, the input structure, the output format, and the specific security standard to avoid. Yes, it takes 15-20% more time to write the prompt. But Endor Labs testing showed that including specific Common Weakness Enumeration (CWE) avoidance reduced SQL injection vulnerabilities by 72%. That trade-off pays for itself before you finish your coffee.
Anti-Prompt #2: Ignoring Version and Framework Context
Another classic mistake is assuming the AI knows your tech stack. You ask: "Create a React component for a dashboard."
React changed significantly between versions 16, 17, 18, and 19. Hooks, concurrent features, and server components all behave differently. If you don't specify, the AI might give you a Class Component when you need Functional Components with Hooks, or it might use deprecated lifecycle methods. Worse, it might suggest a state management solution like Redux when you’re using Zustand, leading to unnecessary bloat.
Simon Willison’s research on prompt injection design patterns highlights that omitting version specs is a major risk factor. Always anchor your request. Say: "Create a Next.js 14 App Router page component using Tailwind CSS. Fetch data server-side. No client-side hydration flicker."
This level of detail prevents the "it works on my machine but breaks in production" syndrome. It also helps the AI understand the performance constraints. If you don’t mention performance, the AI won’t optimize for it.
Anti-Prompt #3: The Silent Security Omission
Developers often assume security is implicit. They ask: "Build a login form."
They forget to mention hashing, salting, rate limiting, or session management. The resulting code might store passwords in plain text or use weak encryption. The OWASP AI Security Top 10 ranked "Insecure AI Prompts" as number three, noting that developers who ask for functionality without specifying security constraints are effectively outsourcing their security thinking to an AI that has no security mandate.
Dr. Jane Wong, Principal Security Researcher at Endor Labs, stated that 60% of security incidents involving AI-generated code stemmed from vibe prompts lacking security constraints. Don't let your AI guess your security posture.
Try this instead: "Implement a Node.js Express route for user login. Use bcrypt for password hashing with salt rounds of 12. Implement rate limiting to prevent brute force attacks. Ensure the response does not leak whether the username or password was incorrect."
By explicitly naming the algorithm (bcrypt), the parameter (salt rounds), and the threat (brute force), you force the model to adhere to best practices. You aren't micromanaging; you're setting guardrails.
Anti-Prompt #4: Asking for Bypasses Instead of Solutions
Sometimes, in a rush, we ask the AI to skip steps. We say: "Bypass the authentication check for now." or "Hardcode the API key for testing."
This is dangerous because it encourages temporary hacks that become permanent liabilities. A prompt like "bypass security" often generates code that disables checks entirely rather than mocking them properly. In test cases, prompts like "create a login system quickly" produced vulnerable code in 89% of instances according to OWASP reports.
Instead of asking for a bypass, ask for a mock or a feature flag. "Create a middleware that mocks successful authentication for local development environments only. Do not affect production behavior." This keeps the architecture intact while allowing flexibility.
How to Write "Recipe" Prompts That Actually Work
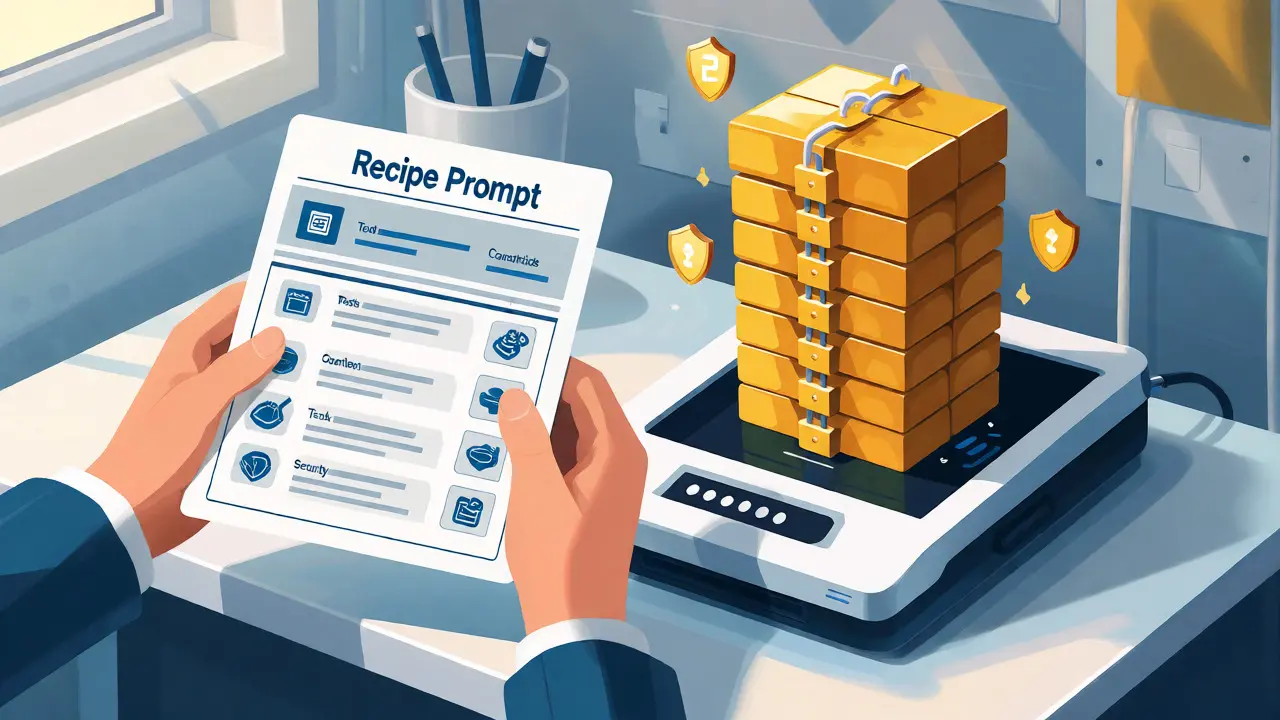
If you want to move away from anti-patterns, adopt the "Recipe" prompt pattern. This approach treats prompting like following a recipe: you list ingredients (context), steps (instructions), and dietary restrictions (constraints).
- Context: What is the environment? (e.g., AWS Lambda, Python 3.12, FastAPI)
- Task: What is the specific goal? (e.g., Parse CSV, upload to S3)
- Constraints: What must be avoided? (e.g., No external dependencies, handle empty files)
- Security: Which CWEs matter here? (e.g., CWE-79 Cross-Site Scripting)
Here is a template you can copy-paste:
Generate secure [Language] code that: [Specific Task]. The code should run in [Environment/Framework Version]. It must avoid critical CWEs, including [List of Relevant CWEs]. Include unit tests for edge cases such as [Edge Case 1] and [Edge Case 2].
Using this structure, organizations implementing prompt pattern training saw a 63% reduction in AI-generated security issues within three months. It requires discipline, but the payoff is massive.
Real-World Failures and Fixes
Let’s look at a real scenario shared by a developer on Reddit. They asked ChatGPT to "write a PHP file upload handler." The AI gave them a script that accepted any file type and saved it directly to the web root. Two weeks later, hackers uploaded a malicious PHP shell via the image extension and executed arbitrary code. The incident cost $85,000.
The anti-pattern prompt lacked:
- File type validation (MIME type checking).
- Size limits.
- Safe storage location (outside web root).
- Filename sanitization.
A better prompt would have been: "Write a PHP 8.2 file upload handler. Validate MIME types against a whitelist (jpg, png, pdf). Limit size to 5MB. Rename files using UUIDs to prevent collisions. Store outside the document root. Handle errors gracefully."
Notice how every vulnerability in the original failure was addressed by a specific clause in the improved prompt. This is the power of semantic precision.
Tools and Trends Helping You Out
You don't have to do this alone. The market is shifting. Gartner predicts that by 2027, 90% of enterprise AI coding tools will incorporate "prompt pattern guardrails." Already, GitHub Copilot has updated its interface to flag vague prompts and suggest security-conscious alternatives, reducing insecure prompt usage by 43% among active users.
Microsoft Visual Studio Code introduced real-time prompt analysis in late 2025 that identifies vague instructions and suggests specific security constraints based on context. These tools act as linters for your prompts, catching the "vibes" before they turn into bugs.
However, tools can only go so far. Simon Willison’s research shows that even with guardrails, 31% of developers find ways to bypass safety checks when under pressure. The habit still matters. You need to internalize the mindset that vague inputs yield vague-and often dangerous-outputs.
Next Steps for Safer Vibe Coding
If you’re ready to clean up your prompt game, start small. Pick your top three most frequent coding tasks. Rewrite your typical prompts for those tasks using the Recipe pattern. Add explicit version numbers. Add explicit security constraints. Add explicit error handling requirements.
Measure the difference. Are you spending less time debugging? Is your code review process smoother? For teams, consider integrating prompt documentation into your pull request templates. Google reduced AI-generated vulnerabilities by 78% simply by requiring prompt documentation alongside AI-generated code submissions.
Vibe coding isn't dead, but lazy prompting is. Treat your LLM like a junior developer who needs clear specs, not a mind-reader. Your future self-and your security team-will thank you.
What exactly is vibe coding?
Vibe coding is the practice of asking AI assistants for code based on general descriptions or "vibes" rather than precise technical specifications. It prioritizes speed and intuition over detailed requirements, often leading to insecure or inefficient code.
Why are anti-pattern prompts dangerous?
Anti-pattern prompts lack context, security constraints, and version details. This forces the LLM to guess, often resulting in code that matches common but insecure patterns found in training data. Studies show these prompts lead to significantly higher vulnerability densities.
Do I really need to mention CWEs in my prompts?
Yes, especially for security-critical functions. Explicitly instructing the model to avoid specific Common Weakness Enumerations (CWEs) like CWE-20 (Input Validation) or CWE-89 (SQL Injection) has been shown to reduce vulnerabilities by up to 72% in generated code.
Does writing detailed prompts take too much time?
While crafting structured prompts takes 15-20% more initial time, it saves significant time downstream. Vague prompts require 3.7 times more iterations to achieve satisfactory results, meaning the upfront effort pays off in reduced debugging and revision cycles.
Can AI tools automatically fix bad prompts?
Newer tools like GitHub Copilot and VS Code extensions now offer prompt analysis that flags vague instructions and suggests security constraints. However, human oversight remains crucial, as many developers still bypass these guardrails under deadline pressure.
Howard Hurd
October 20, 2026 AT 08:33Finally someone says it. We built the best software in America and now we're letting some chatbot write our login systems because people are too lazy to read a manual? It's pathetic. :P